
What is a contingency plan? How to write one in seven steps
Table of Contents
A contingency plan is a written set of actions, named owners, and pre-approved resources that a business switches on when a specific disruption happens, such as a cyberattack or a supplier failure. This guide from ProfileTree explains the main plan types, the steps to write one, and the UK rules that shape it.
What a contingency plan covers
A contingency plan covers one thing above all, which is the gap between the moment something goes wrong and the moment normal work resumes. Without a plan, staff improvise under pressure and lose hours deciding who should act. With one, they follow a sequence that was agreed and rehearsed when nobody was under strain.
A business contingency plan usually records the risks it covers, the event that triggers each response, the steps to take and the person who takes them. It also sets out how staff, customers and suppliers will be told, which backup systems or suppliers are on standby, and when the plan is next reviewed. A good plan reads like instructions a capable stranger could follow on their first day in the job.
How it differs from risk management, business continuity and disaster recovery
These four terms are often used as if they mean the same thing, and the confusion leaves gaps. Risk management lowers the chance that a problem happens at all. A contingency plan switches on when a defined event happens anyway, and business continuity is the wider discipline of keeping the whole organisation running through a serious disruption. A disaster recovery plan is narrower still and deals only with bringing technology back into service.
| Discipline | What it does | When it applies | Typical standard |
|---|---|---|---|
| Risk management | Reduces the likelihood of disruption | Continuously, before anything happens | ISO 31000 |
| Contingency planning | Sets out the response to a specific event | When a named trigger is met | Aligned with ISO 22301 |
| Business continuity | Keeps essential operations running | Through and after a major disruption | ISO 22301 |
| Disaster recovery | Restores IT systems and data | After a technical failure or attack | Part of ISO 22301 planning |
A firm can hold a detailed risk register and still have no tested answer for the day a risk comes true. Our guide to business risk management covers the preventive side in more depth.
Why a tested plan matters to a business
The first hours of an incident decide most of its cost. Lost sales, recovery spending, regulatory penalties and damaged client relationships all grow while a team argues about who is in charge. Having answered those questions in advance means the first hour goes on action.
Customers also judge a business by how it behaves under pressure. A clear holding message, a fast workaround and a named contact keep trust intact, while silence or confusion tends to cost accounts long after the original problem is fixed.
The four types of contingency plans
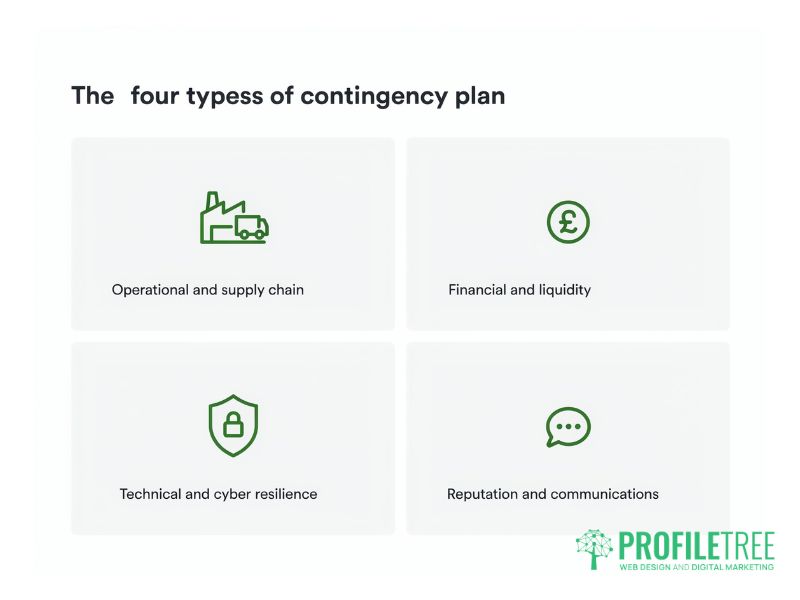
Most businesses need a version of four plans, each grouped by the part of the business they protect, because the triggers, owners and recovery actions differ sharply between them. Writing one generic plan for everything usually means none of the four is detailed enough to use.
Operational and supply chain plans
This plan covers premises, equipment, utilities and suppliers. A single supplier for something the business cannot work without is one of the most common weak points in a small firm. The plan names alternative suppliers, the workarounds already agreed with them, and the minimum level of service you will commit to while the disruption lasts. Where a supplier truly cannot be replaced, the plan says so and records how long you can operate without them.
Financial and liquidity plans
A cash shortfall can close a viable business faster than the incident that caused it. A financial plan records how the business would reach emergency funds, who may approve spending during a declared incident without waiting for the usual sign-off, and the point at which cost controls begin. Ordinary approval rules can block a fast response, so the plan clears that path in advance.
Technical and cyber resilience plans
For most businesses, the sharpest risks now sit in digital systems: the website, email, cloud storage, payment providers and the software staff use every day. A technical plan covers data loss, outages and cyberattacks, with a recovery time objective (the longest a system can be down before the damage becomes serious) set for every critical system. Backups need to be in place and tested before they are needed, and for many firms that is easiest to secure through a website hosting and maintenance service that keeps off-site copies and restores them on request.
Reputation and crisis communications plans
How a business communicates during an incident often shapes how customers recall it later. This plan holds approved holding statements, the names of the people allowed to speak for the business, and the channels used to reach clients, staff, and, where needed, regulators. Our article on crisis management in marketing covers the public-facing side in more detail.
How to write a contingency plan in seven steps
The steps below follow the logic of ISO 22301, the international standard for business continuity management, adapted for small and medium-sized firms in the UK. Each step depends on the one before it, and a shortcut early on tends to surface only during a real incident.
Steps one and two: identify risks and run a business impact analysis
Start by listing every disruption that could plausibly reach your business, including cyber incidents, supplier failures, staff absence, severe weather, utility outages and financial shocks. Score each one for likelihood and impact on a simple matrix so that effort goes where the danger is greatest.
| Likelihood and impact | Minor | Moderate | Major | Critical |
|---|---|---|---|---|
| Almost certain | Medium | High | Critical | Critical |
| Likely | Low | Medium | High | Critical |
| Possible | Low | Medium | Medium | High |
| Unlikely | Low | Low | Medium | Medium |
A business impact analysis (a structured estimate of what each disruption would cost per hour or per day) then puts figures against the high-priority risks. Those figures tell you where to spend first, and they make the case for the backup arrangements in the later steps.
Steps three and four: set trigger points and response procedures
Plans often fail because nobody is sure when to start them, even when the planned response is sound. A trigger must be specific enough that two people would reach the same decision. “The website has been unreachable for more than 30 minutes” is a trigger, while “a serious IT problem” is too vague to act on.
With the triggers agreed, write the response for each high-priority scenario. Set out the actions for the first hour, the first four hours and the first day, the backup system or supplier to switch to, and the message that goes to clients. A line such as “arrange temporary hosting if the server fails” needs a named provider, a contract already in place, and a person who holds the login before it counts as a procedure.
Steps five and six: assign roles with a RACI matrix and test the plan
Every action needs one named owner. A RACI matrix (a table showing who is Responsible, Accountable, Consulted and Informed for each task) makes ownership visible, and it should name a deputy for every key role along with out-of-hours contact details that are kept current.
Testing is where a plan earns its value. A tabletop exercise, in which the team talks through a scenario around a table, costs an afternoon and exposes most of the gaps. A live test, such as restoring the website from last night’s backup to a staging copy, shows whether the technical steps work in practice. Record what went well, where people hesitated and what the plan left out, then fix those points before the next test.
Step seven: maintain and review the plan
Review the plan at least once a year and after any significant change, such as a new system, a key person leaving, a change of supplier, or a merger. After any real incident or test, update it while the lessons are still fresh. Any plan naming software the business stopped using two years ago, or a deputy who has left, will slow the response it was written to speed up.
UK rules and standards that shape a contingency plan
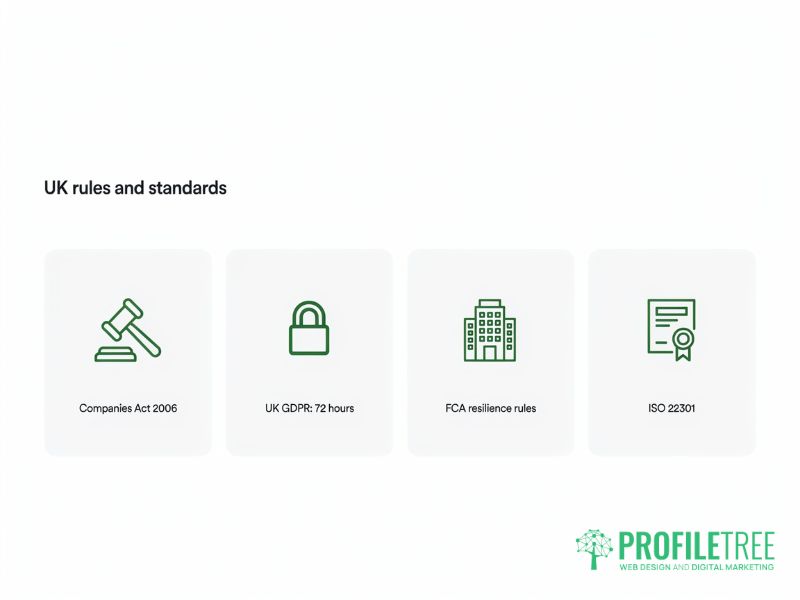
No single UK law requires every business to hold a contingency plan, but several duties make one the practical way to meet them. Directors, firms that hold personal data and certain regulated businesses all carry obligations that a written, tested plan helps to show.
Directors’ duties, UK GDPR and FCA operational resilience
Under section 174 of the Companies Act 2006, directors must exercise reasonable care, skill and diligence, and preparing for foreseeable disruption sits comfortably within that duty. Businesses that handle personal data must report a qualifying breach to the Information Commissioner’s Office within 72 hours of becoming aware of it, where the breach is likely to put people’s rights and freedoms at risk. The ICO’s guide to personal data breaches sets out what to report and when, and your contingency plan should name the person who makes that call. Our GDPR compliance checklist covers the wider data protection groundwork for small firms.
Certain firms regulated by the Financial Conduct Authority have further operational resilience rules to meet, including identifying their important business services and setting the maximum disruption each one can tolerate. Firms in that position should build those requirements into the same plan instead of keeping a separate document.
ISO 22301 and the UK Government Resilience Framework
ISO 22301 is the international standard for business continuity management systems, and contingency planning sits within it. Aligning a plan with its structure gives the business a sound, auditable approach without the cost of formal certification, which most small firms do not need.
The UK Government Resilience Framework, published in December 2022, treats resilience as a responsibility shared by government, public bodies and private organisations. It is aimed mainly at government, though it gives a useful view of the risks the UK plans for nationally.
Planning for website, cloud and AI tool failures
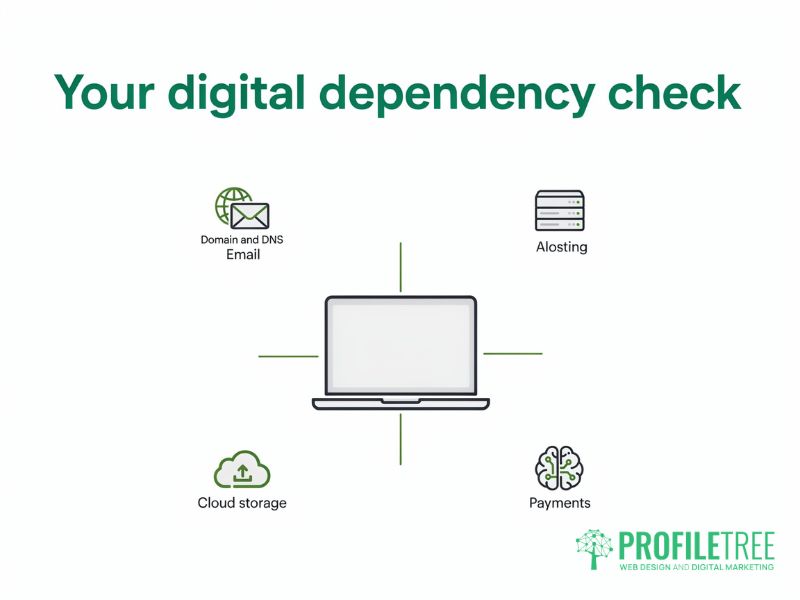
Older contingency plans rarely account for the online services a modern business depends on. A lapsed domain renewal, a hosting outage, a payment provider failure or an AI tool that starts producing wrong output can stop work as surely as a flood. ProfileTree is a Belfast web design and digital marketing agency, founded in 2011 and based at the McSweeney Centre, and these digital failures are the part of a contingency plan we are asked about most.
“Everything ProfileTree builds for a business in Northern Ireland is meant to keep working after the invoice is paid, and that has to include the day something goes wrong. When we talk to a client about website hosting and maintenance, the first question is who acts if the site goes down this afternoon and which backup they restore from. If nobody can answer that in a sentence, the business does not yet have a contingency plan for its website,” says Ciaran Connolly, founder of ProfileTree.
One way to close this gap is a digital dependency check. List every online service the business would struggle to trade without, and record four facts against each one: who owns the account, where the login is kept, how the service would be restored or replaced, and how long the business can work without it. Most owners find at least one service held in a former employee’s name, or a domain registered to a personal email address, and both are easy to fix on a calm day.
| Digital dependency | What to record in the plan |
|---|---|
| Domain name and DNS (the settings that point your domain to your website and email) | The registrar, the account owner, the renewal date, and whether auto-renew is on |
| Website hosting | The provider, how often backups run, where copies are stored and who can request a restore |
| The provider, the admin account and how staff would be contacted if email were down | |
| Payment and booking systems | The provider’s status page, a fallback way to take payment and who contacts the customers affected |
| Cloud storage and business software | The admin account, how data is exported and the alternative tool if the service failed |
| AI tools used in daily work | Which tasks rely on them, how output is checked and how the work would be done without them |
For a WordPress site, the technical half of this check overlaps with ordinary security housekeeping. Our guide to keeping a WordPress site secure covers updates, backups and access control in more detail.
Contingency plan examples and the mistakes to avoid
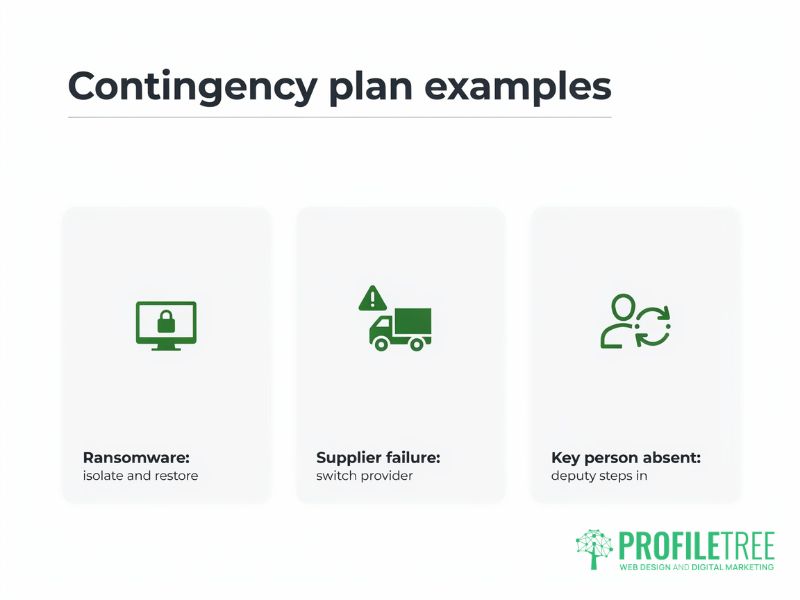
Worked examples make the method concrete. The three scenarios below show how a plan behaves in a live incident, followed by the mistakes that most often undermine a plan that looked sound on paper.
Ransomware attack
This plan starts when business systems have been encrypted and a ransom demand has arrived. The incident lead isolates the affected machines from the network, calls the IT provider and moves staff onto clean devices or a clean copy of the data held off-site. If personal data may have been exposed, the data protection lead starts the 72-hour ICO clock straight away. The team then restores from the most recent backup confirmed to be free of the attack, followed by a security review to close the route the attackers used, and the plan should already say which copy that is and who confirms it is clean.
Loss of a key supplier
Here the response begins once the hosting or logistics provider suffers an outage with no restoration time within the business’s tolerance. The operations lead switches to the secondary provider agreed in advance, moves traffic or orders across, and tells affected clients about any reduced service before they discover it themselves. This scenario shows why the early planning steps matter, because the alternative was arranged long before the outage.
Loss of key personnel
This one applies when the person running a critical client account or system is unavailable for more than 48 hours with no handover in place. The named deputy from the RACI matrix takes over using the documented procedures and contacts the client if service is affected. People are single points of failure in the same way systems are, and documentation and cross-training are the long-term fix.
Common mistakes
Most failed plans fail for the same few reasons. A plan written once and never tested drifts out of date, so it names systems the business no longer uses and people who have left. Vague triggers delay action until the damage is done, and a missing spending authority leaves the team unable to commit money when speed matters most. The other frequent gap is digital: plans that cover fire and flood in detail but say nothing about the website, the domain, or the logins the business runs on.
Getting your website and digital systems ready for a bad day
The next step is to run the digital dependency check above and test one restore, so you know your site and key systems can come back within the time your business can tolerate. If the check shows gaps in backups, access, or monitoring, our hosting team can take on that work, and our digital strategy support can build recovery planning into your wider plans for the website and everything connected to it.
FAQs
1. What are the seven steps of a contingency plan?
They are to identify the risks, run a business impact analysis, set trigger points, write response procedures, assign roles with a RACI matrix, test the plan, and review it on a schedule. The first two steps decide which risks deserve a full response. The middle steps turn each priority risk into a sequence of named actions, and the last two keep the plan accurate as the business changes.
2. What is a contingency plan in simple terms?
A contingency plan is a written set of steps a business follows when a specific problem happens, saying what to do, in what order, and who does it. It differs from a general risk register because it starts working only when a defined event occurs. Most small firms keep it short enough to read in a few minutes during an incident.
3. What are the four types of contingency plans?
They are operational and supply chain plans, financial and liquidity plans, technical and cyber resilience plans, and reputation and crisis communications plans. Each protects a separate area of the business and has its own triggers and owners. Many small firms keep all four in one document with a separate section for each.
4. Is a contingency plan a legal requirement in the UK?
No single UK law requires every business to have a contingency plan, but related duties apply to many firms. Directors must exercise reasonable care under the Companies Act 2006, businesses holding personal data must report qualifying breaches to the ICO within 72 hours under UK GDPR, and certain FCA-regulated firms have operational resilience rules. Rehearsed procedures are the simplest evidence that those duties are met.
5. How does a contingency plan differ from a disaster recovery plan?
A contingency plan covers any disruption across the business, while a disaster recovery plan deals only with getting IT systems and files back. Disaster recovery usually sits inside the wider plan, under the technical type. A business can restore its servers perfectly and still have no answer for a supplier failure or an absent manager.